Find it. Prove it. Fix it.
EchoStrike watches your attack surface, proves what's exploitable with AI-driven attacks, and helps you fix it — continuously, not once a year. It starts with an autonomous pentest, and every finding carries the exact steps that proved it.
Attackers now move at machine speed. Annual testing doesn't.
AI has made attacks faster, cheaper and continuous. A pentest once a year leaves the other 364 days untested. EchoStrike closes that gap — not another scanner, but a system that proves what's exploitable, every day.
Watch the attack surface
Assets, exposures and leaked credentials are rediscovered continuously — not just at the start of an annual test window.
Prove the path, not just the flag
Every finding keeps the steps that demonstrated it, plus a map of what that route actually touches downstream.
Let each side do what it's good at
Automation carries the scale. People carry judgment — authorization calls, ambiguous evidence and decisions that should not be automated.
Find. Prove. Fix. One evidence chain.
Most tools stop at the finding. EchoStrike carries the same evidence from discovery, to a proven attack path, to a fix you can verify — one connected loop rather than disconnected tools.
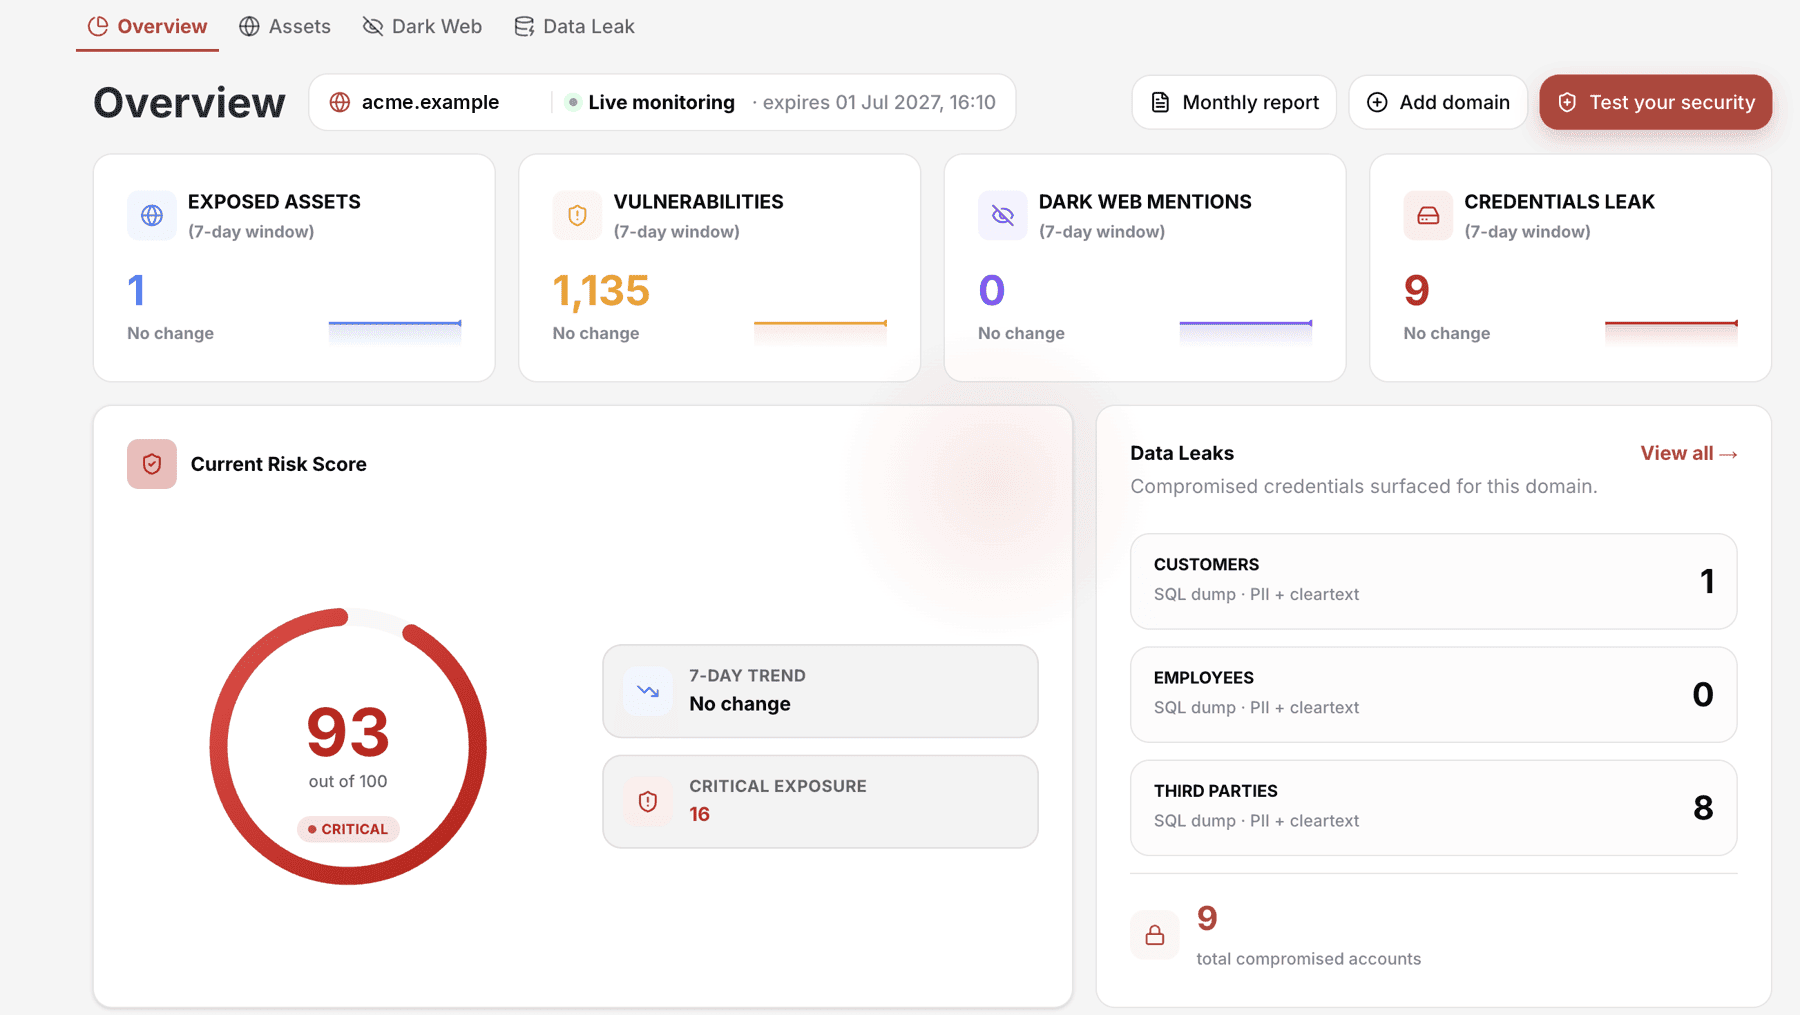
ReconPulse
Your attack surface, scored and watched continuously, worldwide. Every domain carries a live risk score, and leaked credentials are broken out by who they actually expose — customers, employees, third parties — not just matched to a breach list.
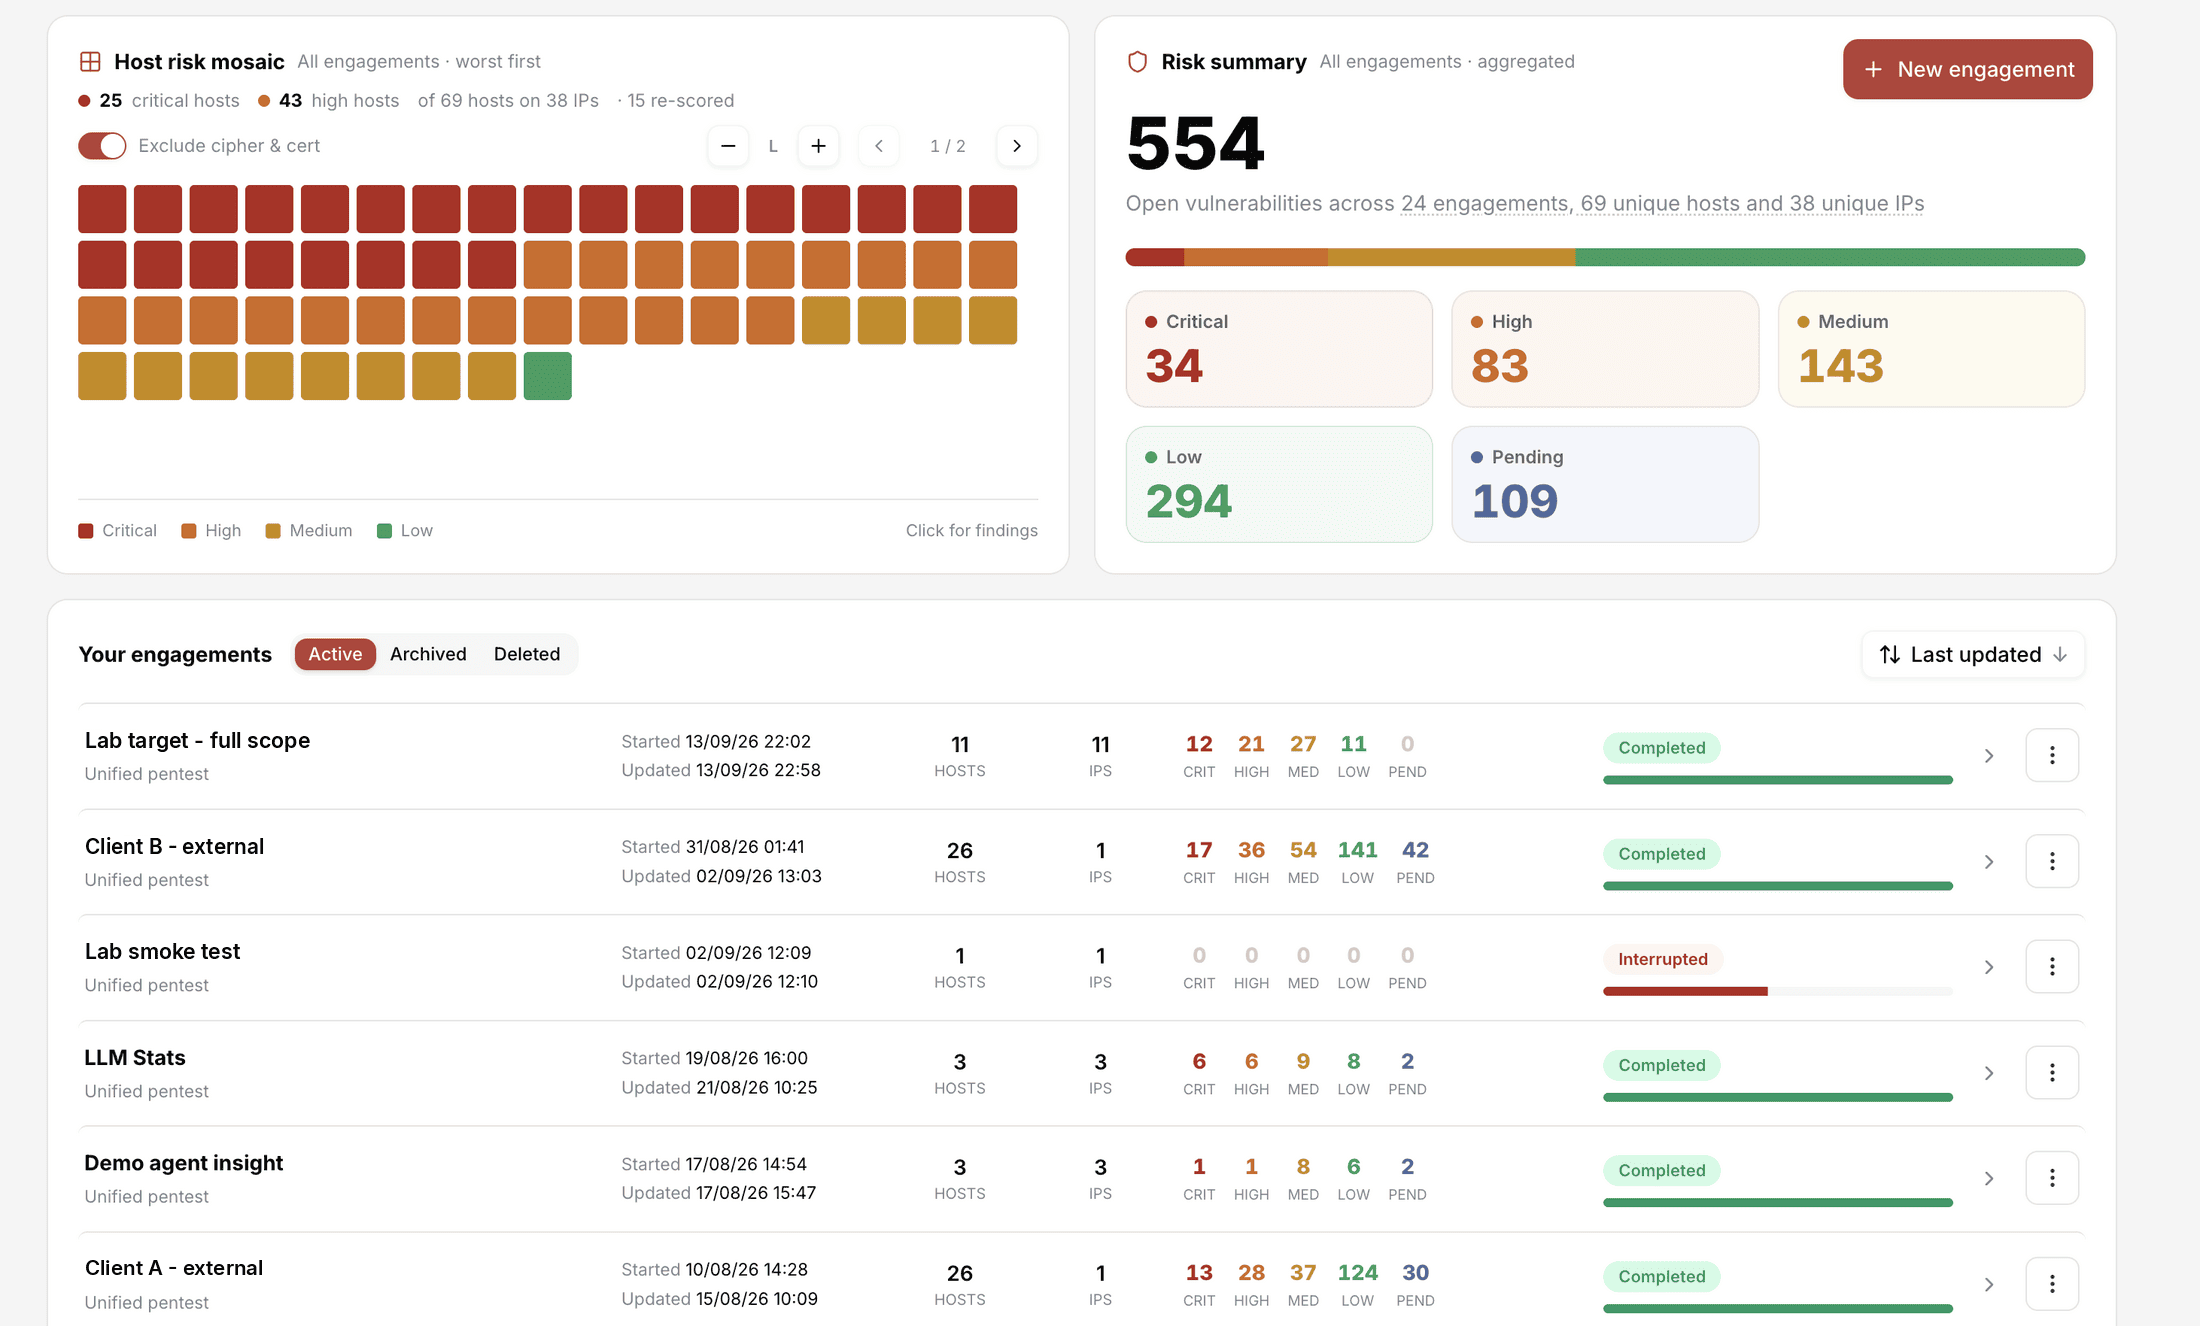
RedEngine
Findings that prove themselves. Every host across every engagement lands on a risk-scored mosaic, rolled up into one live view of what's critical, what's fixed and what's still open — and every finding keeps the exact steps that demonstrated it, plus an AI-generated briefing you can hand straight to the team that has to fix it.
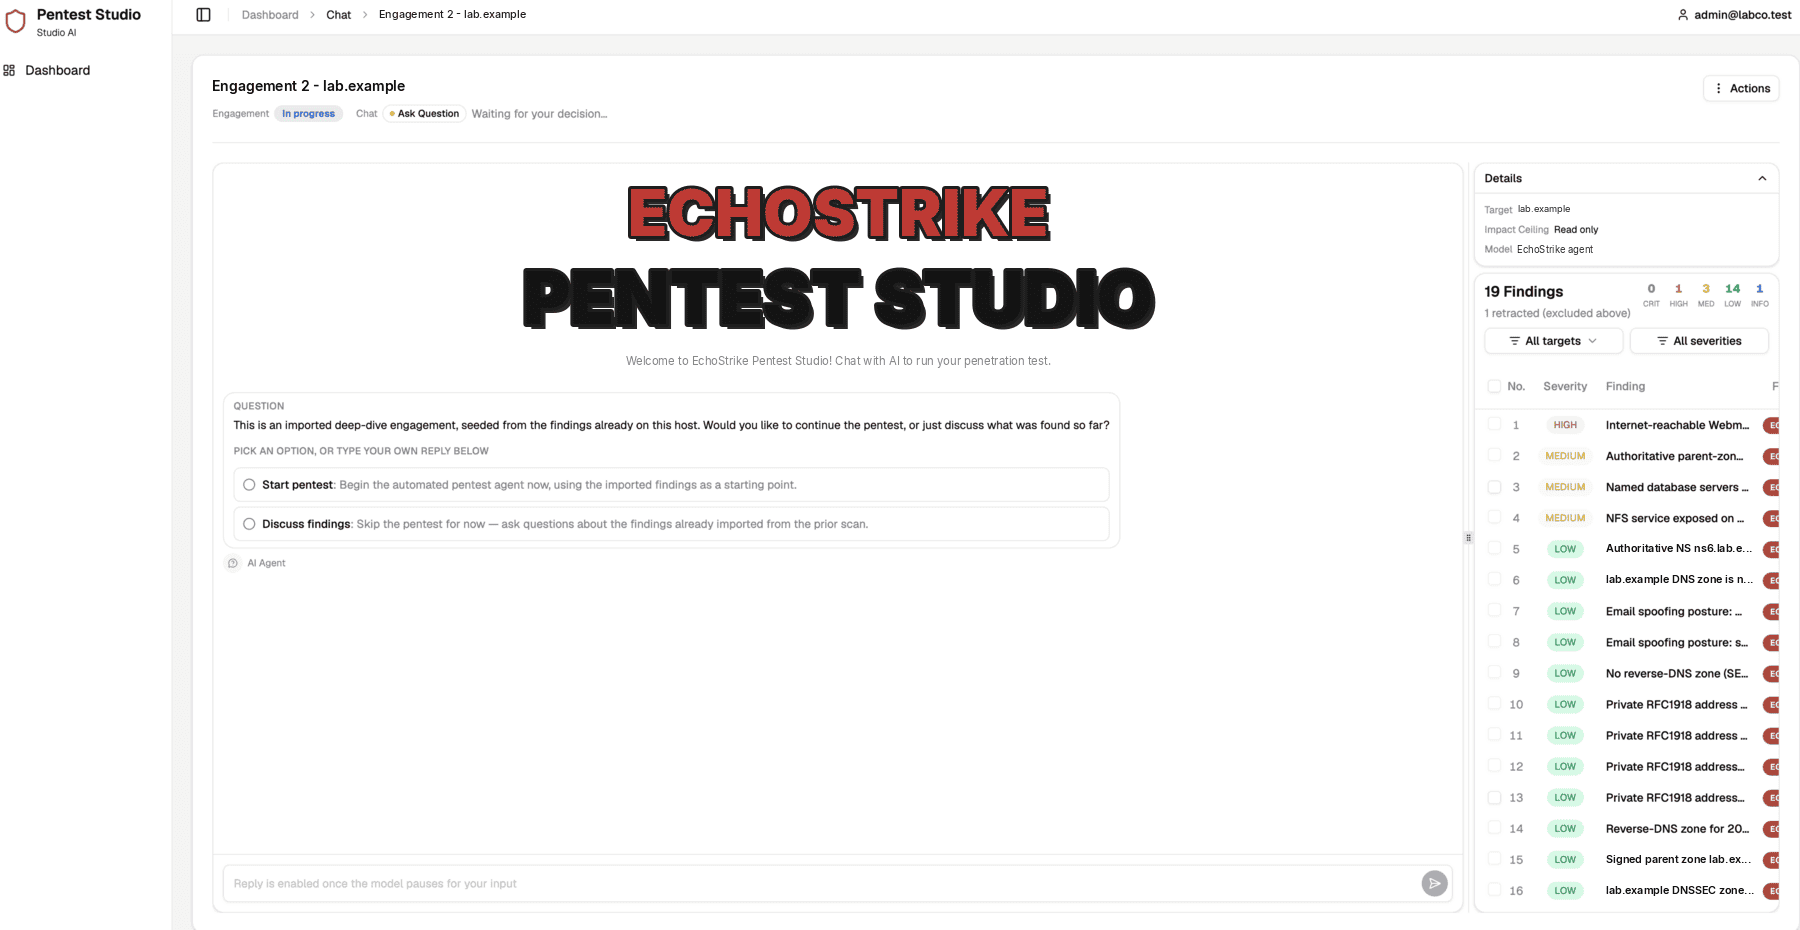
Pentest Studio is RedEngine's own operator console. Open any finding straight into it — same target, same evidence, same engagement history carried forward. Replay a step, push a follow-up scan, or read the full command trace without re-explaining anything.
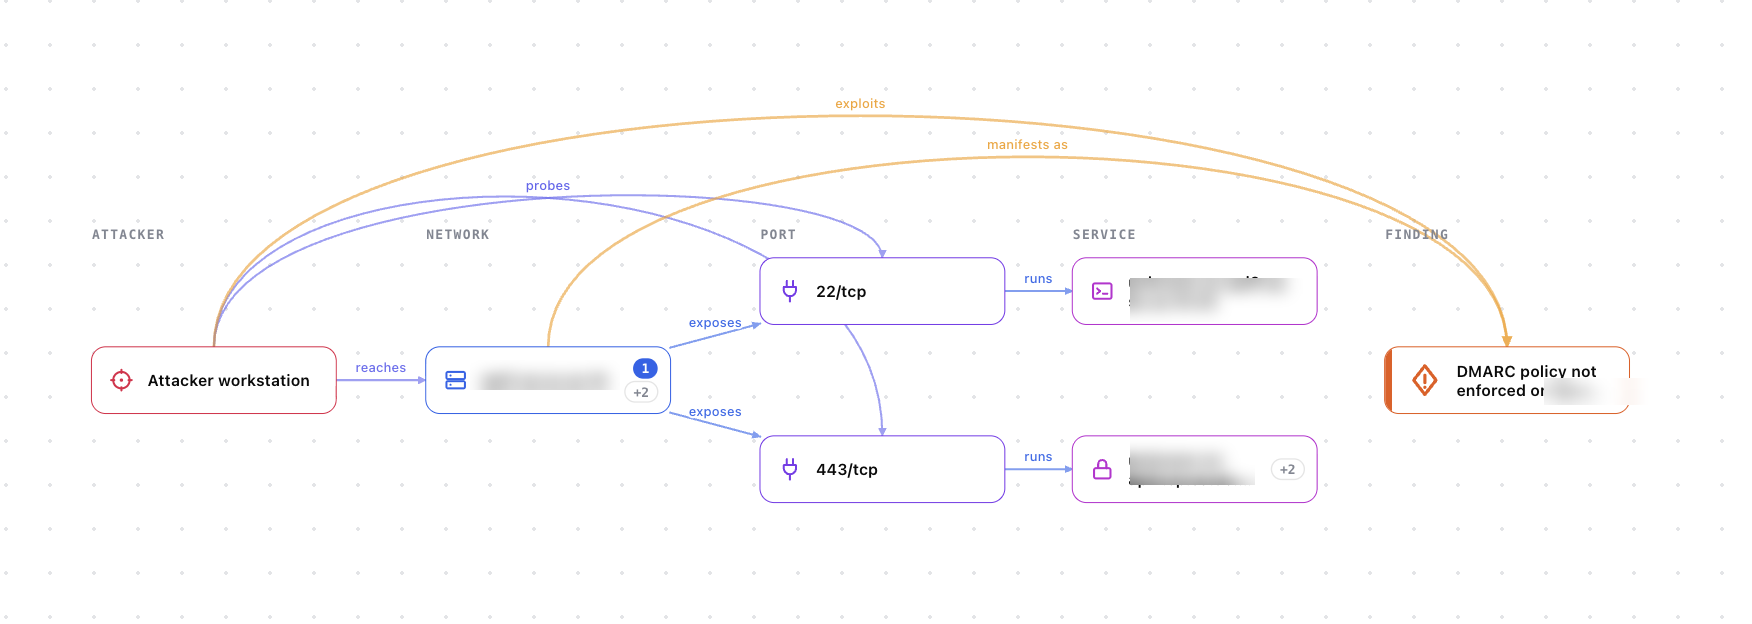
A severity score tells you how bad. This shows you where — every port, service and endpoint reachable from the same evidence, traced all the way to the finding it produces, so a fix can be scoped correctly.
BlueFence
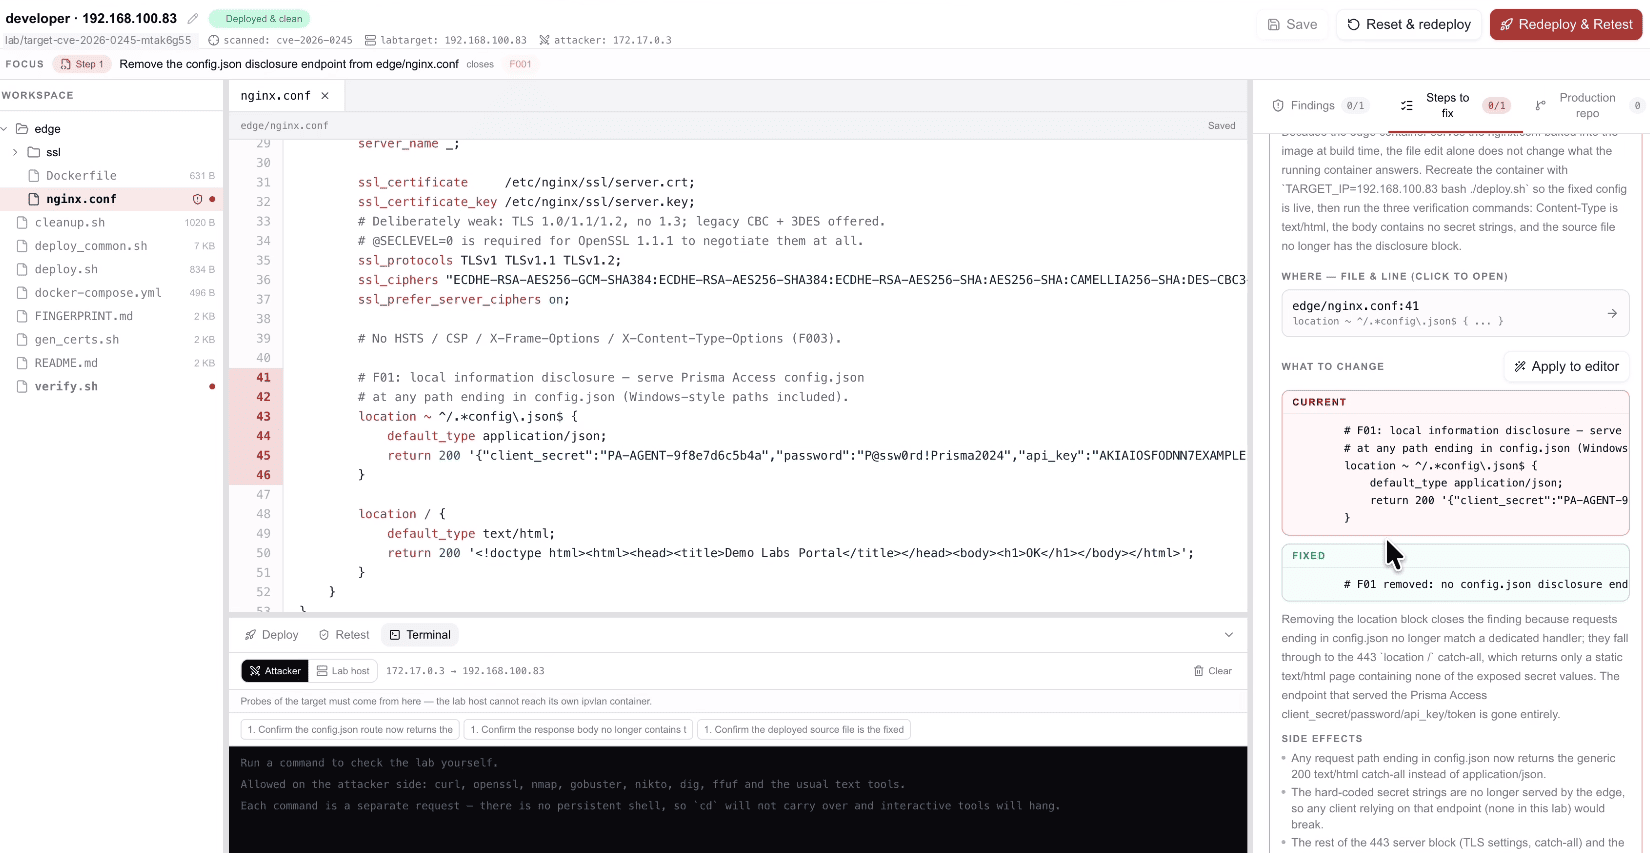
BlueFence closes the loop by re-running the attack that proved the finding — inside a digital twin, not production. The control model checks both sides: the attack fails while the service still responds normally.
Gets smarter with every engagement
Underneath ReconPulse and RedEngine sits Crimson Nexus, EchoStrike's self-improving knowledge base. Every engagement compounds intelligence, so each subsequent test starts faster, digs deeper and reasons better than the last.
Trusted by enterprise, professional-services and public-sector teams in Thailand.
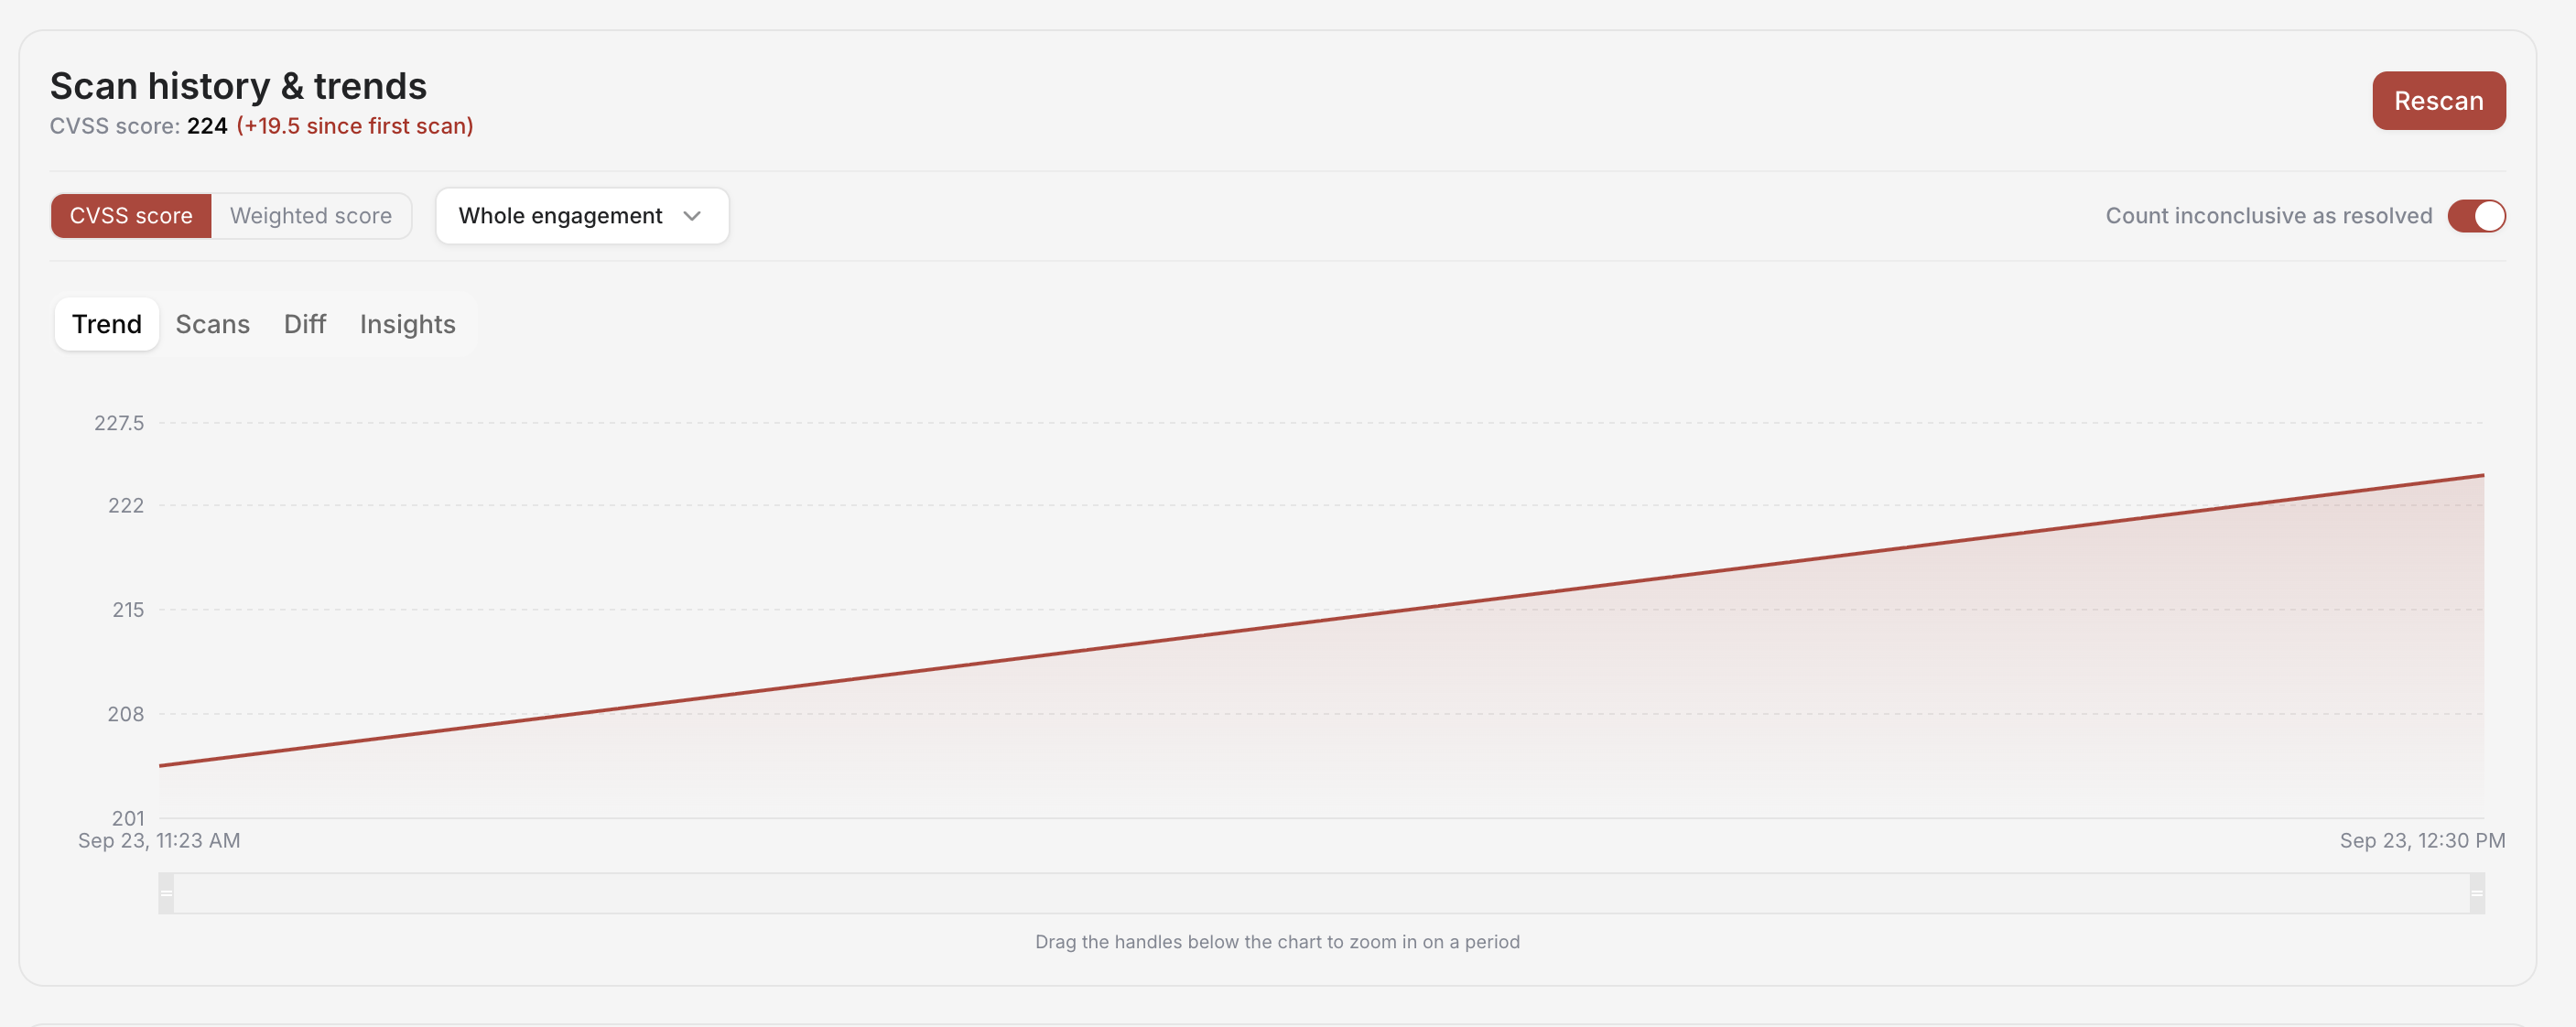
What a one-time test would have missed.
A single scan tells you what's visible today. Continuous validation keeps going. In this engagement, repeated RedEngine passes kept confirming exposure the first pass hadn't reached — adding 19.5 points of confirmed CVSS exposure within the same engagement. A one-off assessment would have closed the book after scan one.
Where the coverage actually comes from
| Traditional pentest | Scanner | AI-assisted tool | EchoStrike | |
|---|---|---|---|---|
| Continuous testing | ||||
| Real exploit validation | partial | |||
| Fail-closed evidence gates (can refuse a finding) | manual | built in | ||
| Attack-path & blast-radius context | manual | varies | built in | |
| Human expert oversight | varies | |||
| Re-test on demand | manual | |||
| Verified remediation (digital twin proves the fix) | manual | in development | ||
| Reasoning that compounds over time | built in |
Offensive power, engineered restraint.
Autonomous offensive tooling needs explicit boundaries. EchoStrike's operating model centers authorization, scope enforcement and human intervention wherever judgment is required.
Scope enforcement
Operate inside authorized boundaries and exclude out-of-scope assets by design.
Non-destructive by default
Agree exploitation depth before testing starts and gather proof without unnecessary disruption.
Human authorization gate
Escalate high-judgment actions and ambiguous evidence to an accredited expert.
Segregated engagement data
Keep client engagement data isolated while learning from higher-level patterns.
Fits how security teams actually operate.
Technology is only half the procurement conversation. EchoStrike is built to slot into existing operations, not replace them.
Flexible deployment
Run continuous or scheduled validation against internal or external attack surface, on the cadence your operations calendar allows.
API-ready workflows
Findings and evidence are available via API, ready to flow into the ticketing and remediation systems you already use.
Compliance-ready evidence
Every finding keeps its full evidence chain and sign-off history, exportable in the format your audit workflows expect.
A named engagement lead
Every deployment has an accountable human point of contact for scope changes, escalations and sign-off.
Autonomy that has to prove itself.
The research frontier is not more automation. It is autonomy that stays within agreed limits, acts only on evidence, and leaves a record an auditor can check. The platform already refuses unproven findings and re-tests on demand; ATVE is the research into measuring and governing the rest.
Decades of offensive security, now built into software.
Offensive-security operators, a PhD-led AI research team and seasoned security leaders, working from Bangkok and Oxford. The expertise that once came only as a consulting engagement now runs continuously in EchoStrike.
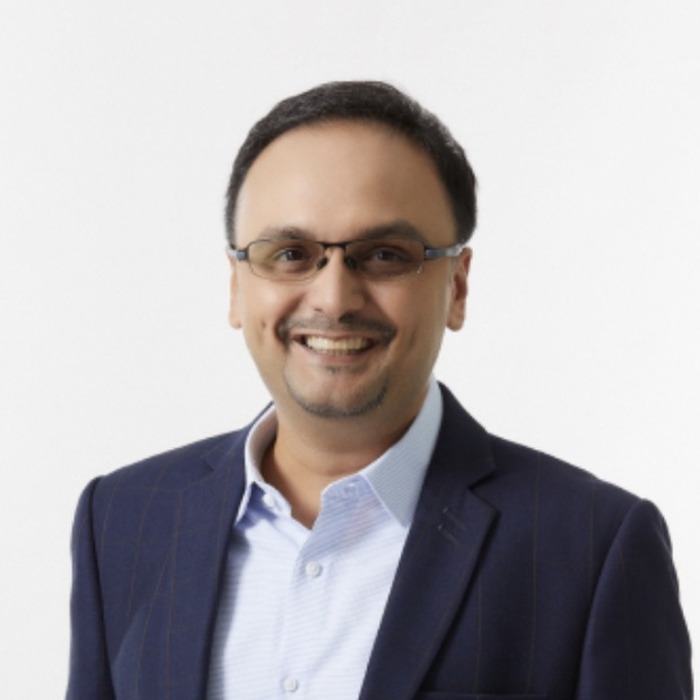
Dr. Varin Khera
25+ years securing telecom and critical infrastructure. Inventor of ATVE.
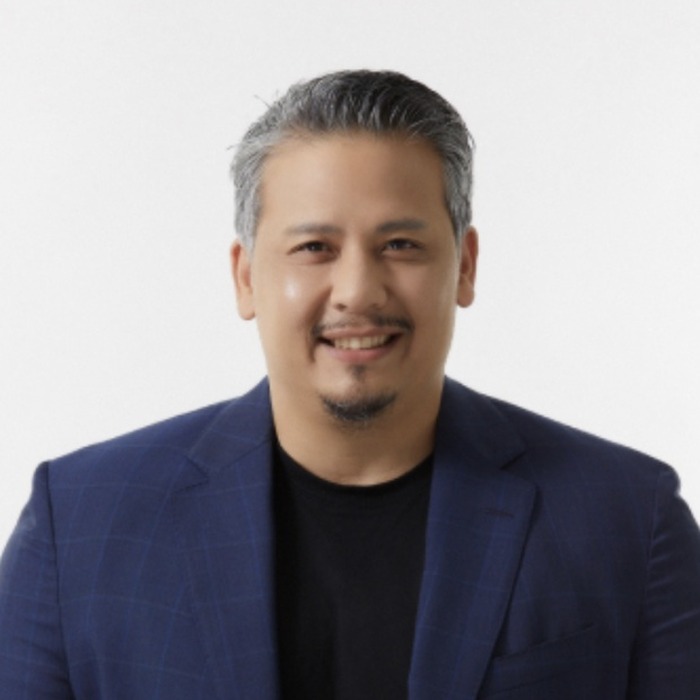
Chris Puranasamriddhi
16+ years in corporate development, capital strategy and cross-border ventures.
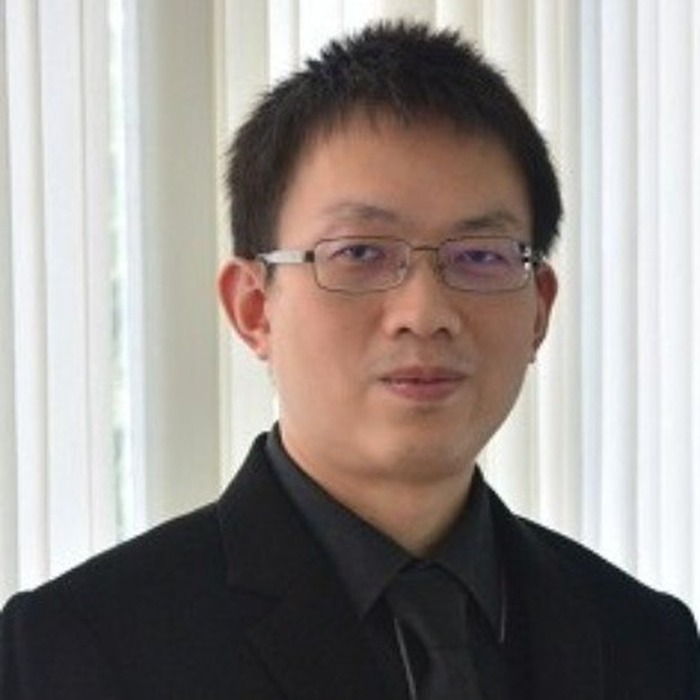
Dr. Pinyo Taeprasartsit
20+ years in AI research. PhD, Penn State. 30+ peer-reviewed papers.
Kusol Watchara-Apanukorn
10+ years of red teaming and 0-day research. CVEs in Fortinet and Lenovo.
Find it. Prove it. Fix it.
Bring your attack surface, testing cadence and remediation problem. We'll show you how EchoStrike finds, proves and helps fix what attackers can actually reach — in your real operating environment.